Ninja Forms’ file upload add-on has its second serious security flaw this year. A newly disclosed vulnerability — CVE-2026-92820, rated CVSS 8.1 (High) — lets attackers with no login read, write, or delete arbitrary files on sites that route form uploads through an external store like Amazon S3. The fix is simple: update the File Uploads add-on to version 3.3.35 or later.
Here’s the catch that matters most: most Ninja Forms users are NOT affected. This flaw only applies to the paid File Uploads add-on and only when your forms use the External File Upload action (S3 or similar external storage). If neither is true for you, there’s nothing to do — but the five-minute check below is worth doing once.
No public exploit code has been confirmed for this flaw, and it is not listed in the CISA Known Exploited Vulnerabilities catalog. In other words: this is a disclosed, patch-now situation, not an active-attack emergency — but it’s a serious flaw in a widely installed add-on, and you should not sit on it.
What the flaw is
Per the TheHackerWire disclosure, Ninja Forms – File Uploads in all versions up to and including 3.3.34 is vulnerable to arbitrary file operations through its external (Amazon S3) upload flow.
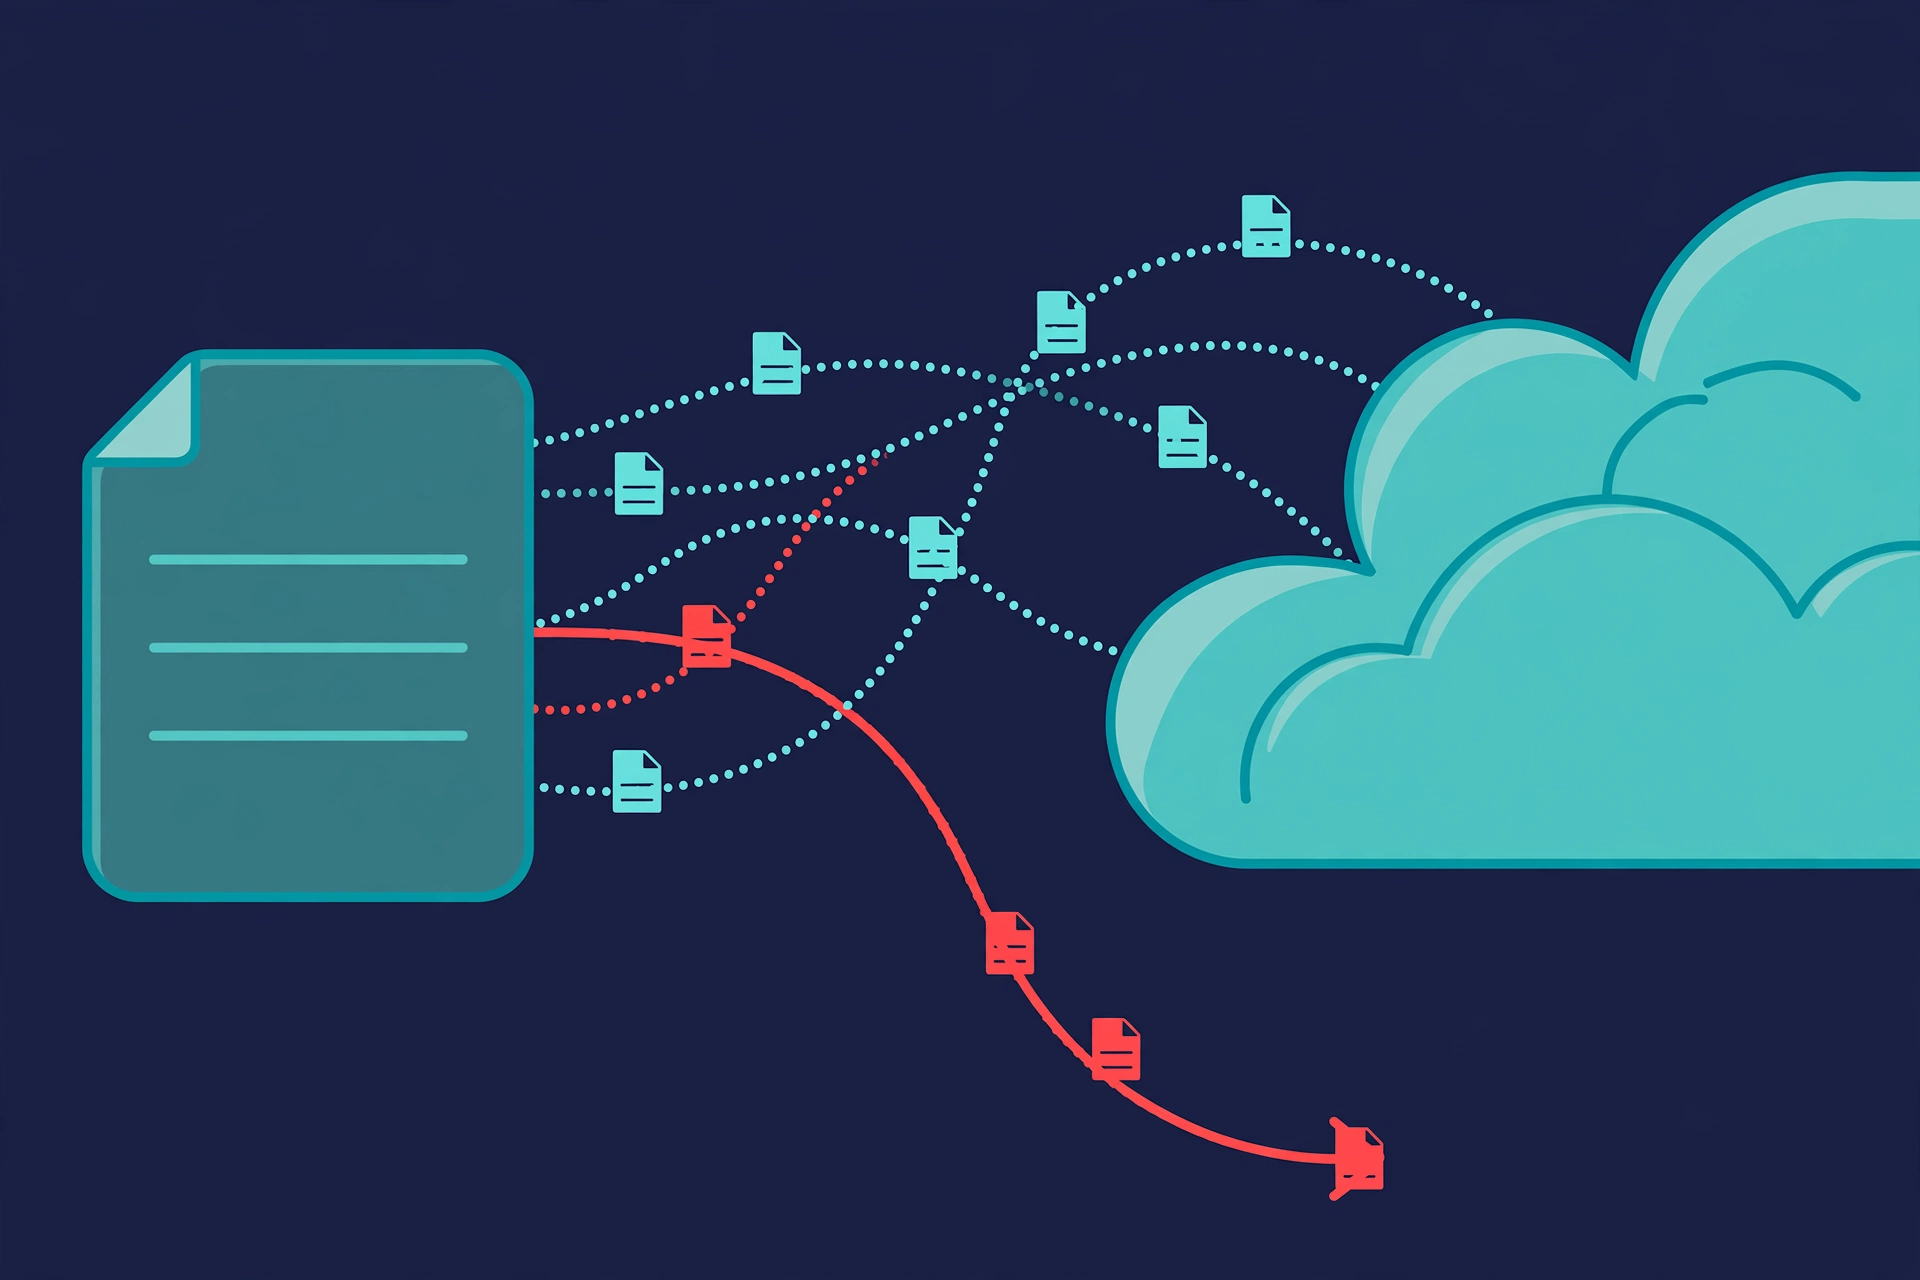
The root cause is deceptively simple: when a form submission comes in, the plugin takes the file path supplied by the visitor and stores it as the upload’s file_path — without validating it. That untrusted path is then used in three places:
- Arbitrary file read — the path is used when the plugin attaches the uploaded file to the form’s notification email, so an attacker can point it at any file on the server (like wp-config.php, which holds your database password) and get it emailed to themselves. This variant additionally requires the form to have an Email action configured to attach the uploaded file.
- Arbitrary file write — fetched content can be written to any path the attacker chooses. When the external store is configured, this can escalate to remote code execution (RCE) — full takeover of the server.
- Arbitrary file deletion — the same untrusted path feeds into a scheduled cleanup, allowing files to be deleted.
Two properties make this bad: it’s unauthenticated (any visitor can submit a form) and the file operations are arbitrary (the attacker picks the target file, not the plugin).
Who’s affected
You need all three of these to be vulnerable:
- You use Ninja Forms (the core form builder), and
- you have the paid File Uploads add-on installed at version 3.3.34 or older, and
- at least one of your forms uses the External File Upload action (sending uploads to Amazon S3 or another external store).
If you use Ninja Forms without the File Uploads add-on, you are not affected. If you have File Uploads but store files locally on your server (the default), you are not affected either. This is a narrow flaw — but a deep one for the sites inside its blast radius.
The older flaw from April — CVE-2026-0740 (CVSS 9.8, Critical) — was different: it affected the add-on’s local upload handling and was actively exploited within days of disclosure. The new CVE-2026-92820 is a separate bug in the external/S3 flow, fully patched in 3.3.35 per WPScan. If you updated promptly in the spring and are still on a recent version, you’re only one update behind.
Step 1: Check whether you’re affected
This takes a few minutes:
- In your WordPress dashboard, go to Plugins → Installed Plugins and look for File Uploads (the Ninja Forms add-on). The version number is printed under the name.
- In Ninja Forms, open your forms and check whether any File Upload field is tied to an External File Upload action (Ninja Forms → Forms → your form → Emails & Actions).
- If both are true — File Uploads 3.3.34 or older and an external/S3 upload action — you’re vulnerable.
Step 2: Update to 3.3.35 or later
The fix, per WPScan, is to update Ninja Forms – File Uploads to version 3.3.35 or later. Before updating anything, take a backup — most hosts offer one-click backups, and the update itself takes about a minute:
- In Plugins → Installed Plugins, click Update now under the File Uploads add-on (or use Dashboard → Updates).
- Confirm the version now reads 3.3.35 or higher.
That’s the whole fix. Version 3.3.34 itself (released September 22, 2026) only strengthened file-type validation — it did not fix this flaw, so double-check you’re past it.
Step 3: Look for signs of trouble
Since the flaw is unauthenticated and the flaw has been public since October 2, a quick sanity check is worth it if you were running a vulnerable setup:
- Users → All Users — look for administrator accounts you didn’t create.
- Your uploads directory and form upload folders — look for files you don’t recognize (especially .php files where they don’t belong).
- Recent emails — if your forms attach uploads to email actions, check whether any notifications contained files you don’t recognize.
- Odd behavior — surprise plugins, redirects, or password-reset emails you didn’t request.
If anything looks off, work through our WordPress security guide — and restore from a backup taken before the suspicious activity rather than cleaning files by hand.
Hardening pointers (for everyone, not just Ninja Forms users)
This flaw is the third serious WordPress story we’ve covered in a week — alongside the SC self-healing backdoor and the wpForo SQL injection. A pattern is emerging, and it’s always the same advice:
- Update plugins promptly. Unpatched plugins are the single most common way WordPress sites get compromised. Enable auto-updates for plugins you trust, or check Dashboard → Updates weekly.
- Don’t install what you don’t use. Every add-on is attack surface. If you don’t send uploads to S3, don’t enable the External File Upload action.
- Keep real backups. Confirm you can actually restore them. A backup you can’t reach is decoration.
- Use a security plugin with a firewall. Our WordPress security guide walks through the full checklist, from backups to login protection.
Sources
- CVE-2026-92820 — TheHackerWire — disclosure details: CVSS 8.1 (High), affected versions ≤ 3.3.34, external S3 upload flow, attacker-supplied file path; no public exploit confirmed; not in CISA KEV.
- WPScan — File Uploads plugin vulnerabilities — fixed in 3.3.35, CVSS 8.1 (High), published 2026-10-01.
- Rapid7 — CVE-2026-92820 — independent confirmation of the affected versions and attack requirements.
- Ninja Forms File Uploads changelog — 3.3.35 is the current release; 3.3.34 (Sept 22, 2026) only strengthened file-type validation.
- WPSentry — WordPress Vulnerability Report, Sept 25 – Oct 2, 2026 — CVE-2026-92820 listed as high severity, affected ≤ 3.3.34.
- Wordfence — CVE-2026-0740 analysis (April 2026) — the older Ninja Forms File Uploads flaw (patched in 3.3.27).